ISO 27001 Information Security Consulting
ISO/IEC 27001 is the international standard for information security management systems (ISMS). Paradygm Consulting helps organizations in Canada and the United States build an ISMS and prepare for accredited certification to ISO/IEC 27001:2022, with fixed-cost consulting and guaranteed certification support (subject to agreed scope and client cooperation).
Whether you need a focused gap analysis, documentation, staff training, internal audits or full support through your certification body’s audit, our team has guided organizations through ISO-based certifications for 25+ years.
Call 1-855-702-9001 · Email info@paradygm.co · Offices in Thornhill, Ontario and Coral Springs, Florida
What is ISO/IEC 27001?
ISO/IEC 27001 is published jointly by ISO and the International Electrotechnical Commission (IEC); “ISO 27001” is the common short name for the same standard. It sets out what an ISMS must do to identify information security risks and keep them under control, so that the information your organization owns or handles stays confidential, accurate and available when it is needed, whether it is on paper, on your own systems or in the cloud.
The current edition is ISO/IEC 27001:2022, published in October 2022. Amendment 1, published in 2024, added climate action changes. Accredited certificates to the older 2013 edition had to move to the 2022 edition by 31 October 2025, so certification today is to ISO/IEC 27001:2022.
Benefits of ISO 27001 certification
Give customers and partners independent evidence that you manage information security risk
Answer supplier security questionnaires and contract clauses that ask for a certified ISMS
Reduce your exposure to cyber-attacks, data loss and privacy incidents with planned risk treatment
Protect information in every form: paper, on-premises systems and cloud services
Bring security policies, roles and controls together in one managed framework
Integrate with ISO 9001, ISO 14001 and ISO 45001 on a common management system structure
How the standard is organized
Like ISO 9001, ISO 14001 and ISO 45001, ISO/IEC 27001 follows the common ISO management system structure:
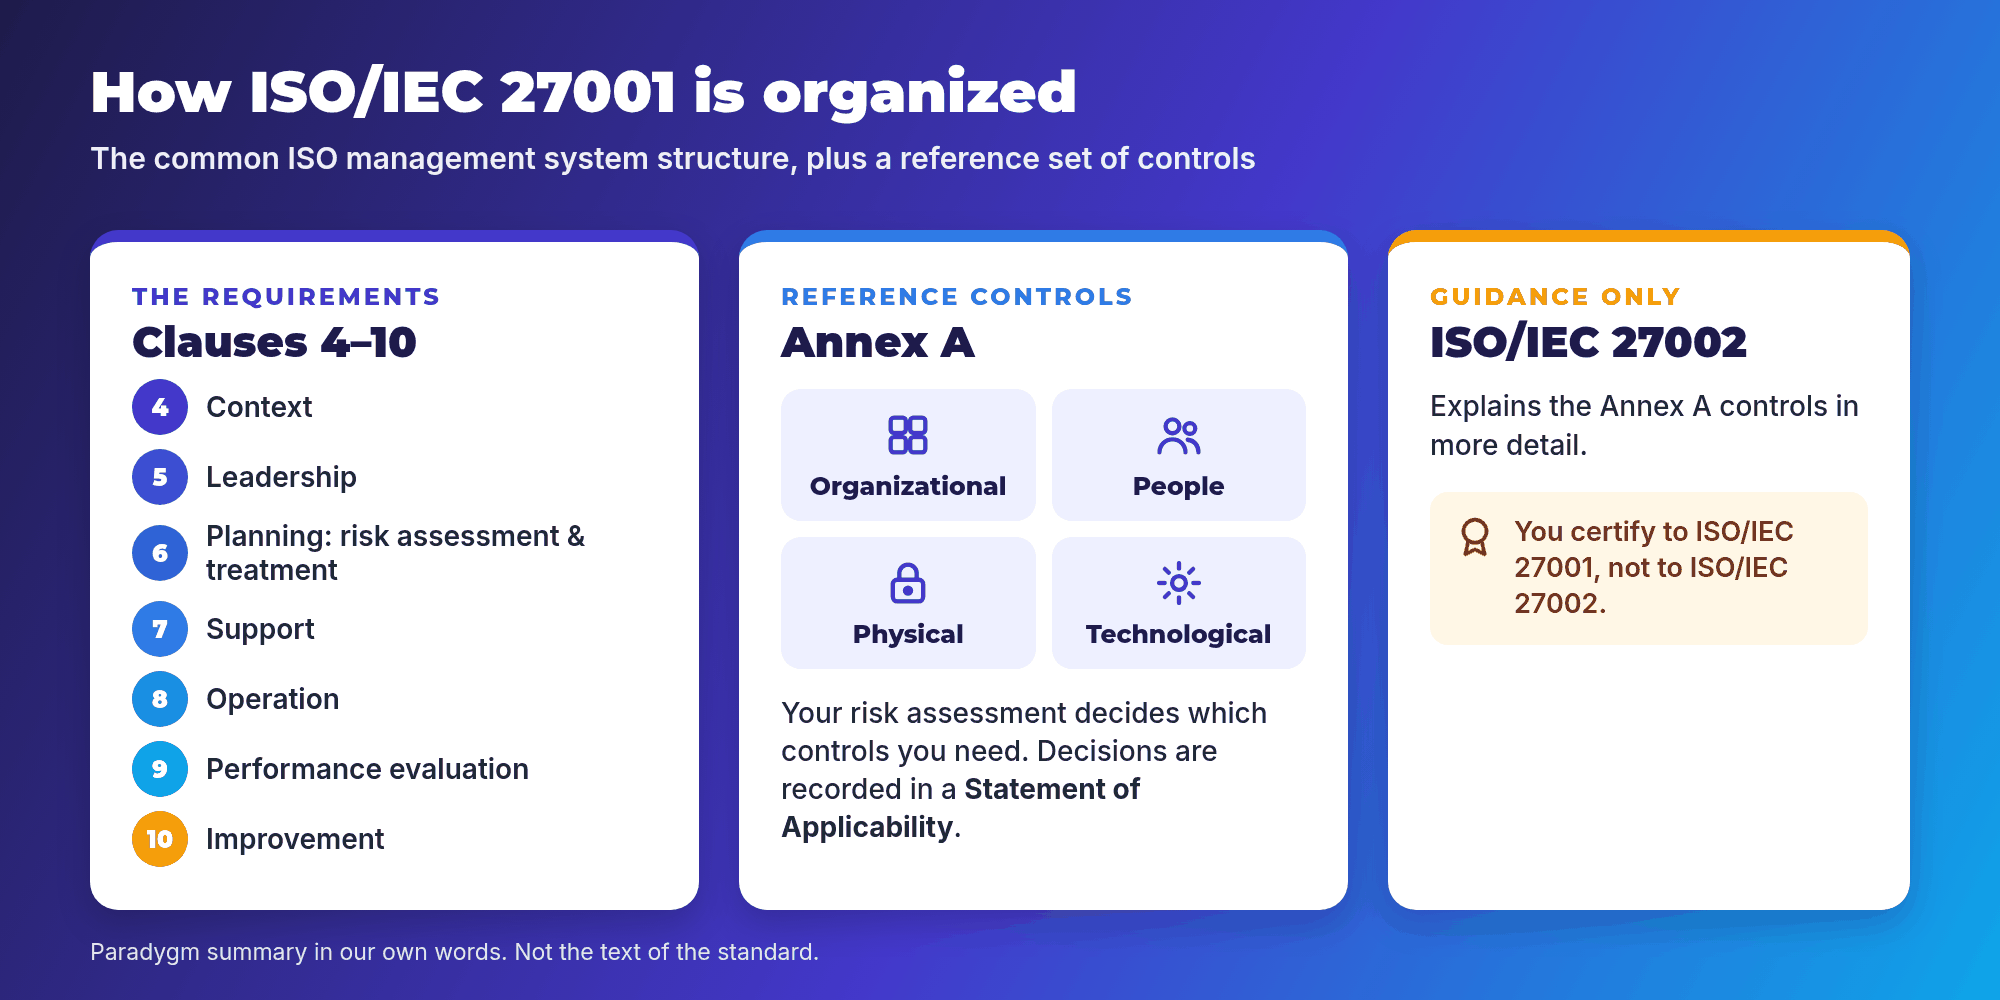
Clauses 4–10: context, leadership, planning (including information security risk assessment and risk treatment), support, operation, performance evaluation and improvement.
Annex A: a reference list of information security controls, grouped into organizational, people, physical and technological themes. You decide which controls you need through your risk assessment and record those decisions in a Statement of Applicability.
ISO/IEC 27002: a separate guidance standard that explains the Annex A controls in more detail. Organizations certify to ISO/IEC 27001, not to ISO/IEC 27002.
Who should consider ISO 27001
IT service providers, software and cloud companies, and managed service providers
Organizations that store or process customer, employee or personal data
Suppliers whose customers now require a certified ISMS in contracts or questionnaires
IT asset disposition (ITAD) and R2v3 electronics recyclers that handle data-bearing devices
Manufacturers and aerospace suppliers that protect customer drawings and technical data
Organizations already certified to ISO 9001 that want one integrated management system
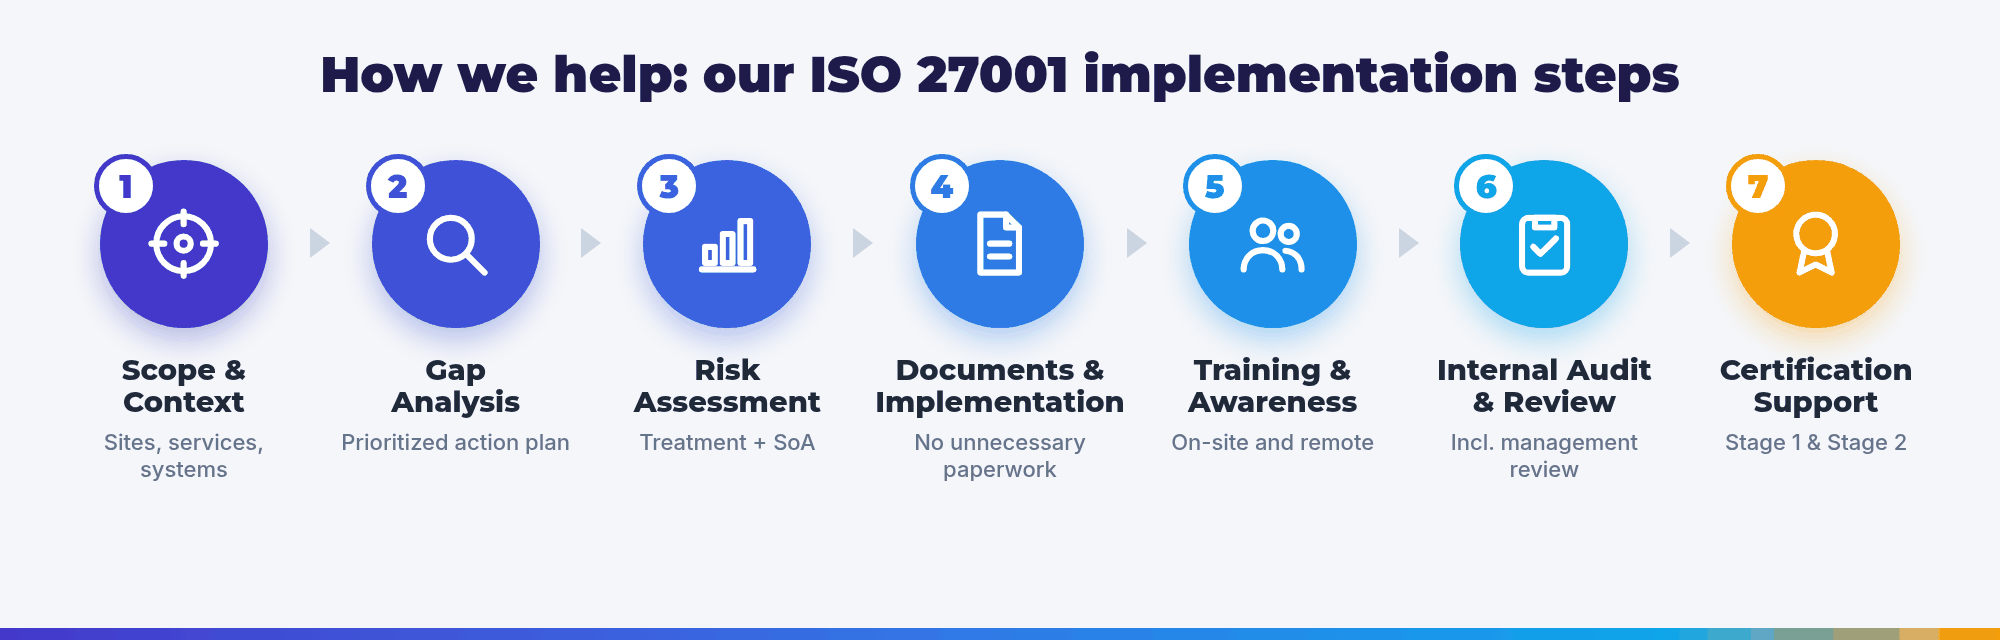
Our ISO 27001 implementation steps
1. Scope and context
Agree the ISMS scope (sites, services, systems and people), and identify the interested parties and requirements that matter to you, including legal, regulatory and contractual obligations.
2. Gap analysis
We assess your current security practices against ISO/IEC 27001 and produce a prioritized action plan: what already works, what needs updating and what is missing.
3. Risk assessment and treatment
We help you set up a practical risk assessment method, choose the controls that treat your risks and prepare your Statement of Applicability.
4. Documentation and implementation
Develop the policies, procedures and records the ISMS needs, and put the selected controls into everyday practice without unnecessary paperwork.
5. Training and awareness
Leaders, process owners and staff need to understand their security responsibilities. Paradygm delivers on-site and remote training.
6. Internal audit and management review
Confirm the ISMS works in practice before the certification body arrives. We perform internal audits and facilitate management review.
7. Certification support
We help you select an accredited certification body, prepare for the Stage 1 and Stage 2 audits, and close any findings efficiently.
Fixed-cost consulting fees are available for defined scopes. Guaranteed certification support applies when the agreed scope is followed and the organization implements required actions in good faith before the certification audit.
Why Paradygm for ISO 27001
25+ years helping organizations achieve and maintain ISO-based certification
Over 200 clients successfully certified
Canada and United States coverage — Thornhill, Ontario and Coral Springs, Florida, with remote and on-site support
Multi-standard depth — ISO 9001, ISO 14001, ISO 45001, ISO 13485, AS9100 family, R2 and related standards
Integrated management system experience, so information security fits the systems you already run
Clear commercial model — fixed-cost consulting fees and guaranteed certification support paired with defined scope and client cooperation
We are consultants and auditors, not a certification body. Our role is to get your ISMS ready so the certification audit succeeds; your accredited certification body issues the certificate.
Frequently asked questions — ISO 27001
What is the current edition of ISO 27001?
ISO/IEC 27001:2022, published in October 2022. Amendment 1 (2024) added climate action changes.
Our certificate is still to ISO/IEC 27001:2013. Is it valid?
The transition period for the 2013 edition ended on 31 October 2025, and certificates to the 2013 edition were to expire or be withdrawn at that point. If yours was not transitioned, talk to your certification body about certifying to ISO/IEC 27001:2022. We can run the gap analysis.
Do we have to implement every Annex A control?
No. You determine which controls you need through your risk assessment and treatment, and you justify what is included and excluded in your Statement of Applicability.
Can ISO 27001 be combined with ISO 9001 or other standards?
Yes. Because ISO/IEC 27001 shares the ISO management system structure, document control, internal audit, management review and corrective action can be run once for all your certified standards.
How long does an ISO 27001 project take?
It depends on your scope, number of sites and how mature your current security practices are. We provide a schedule with the proposal after the gap analysis.
What does “guaranteed certification” mean at Paradygm?
When you engage Paradygm under an agreed scope and implement the actions we identify, we stand behind our consulting support through certification. Guarantee terms are defined in the proposal and depend on client cooperation, timely implementation and scope boundaries. Your accredited certification body remains the independent issuer of the certificate.
How do I get started?
Call 1-855-702-9001, email info@paradygm.co, or request a quote. We will schedule a discovery call, outline a gap analysis and propose a fixed-cost path to ISO/IEC 27001:2022 certification.
Ready to start your ISO 27001 project?
Start with a clear gap analysis and a realistic schedule for your certification audit.
Paradygm Consulting ISO 27001 consulting for Canada and the United States
Phone: 1-855-702-9001 · Email: info@paradygm.co · Consulting services · Request a quote
Sources for standard status and transition dates: ISO (iso.org/standard/27001) and IAF MD 26 transition requirements for ISO/IEC 27001:2022. Always confirm audit timing with your accredited certification body. This page is a summary in Paradygm’s own words and does not reproduce the standard; buy ISO/IEC 27001 from ISO or your national standards body.